Network security • Firewall • Threat protection

Protect your business network from modern threats.

Strengthen your IT infrastructure with professionally deployed firewall and network security solutions from Hyper-Access Solutions.

From perimeter protection and secure internet access to network segmentation, traffic control, and remote connectivity, we help businesses build safer and more manageable network environments.

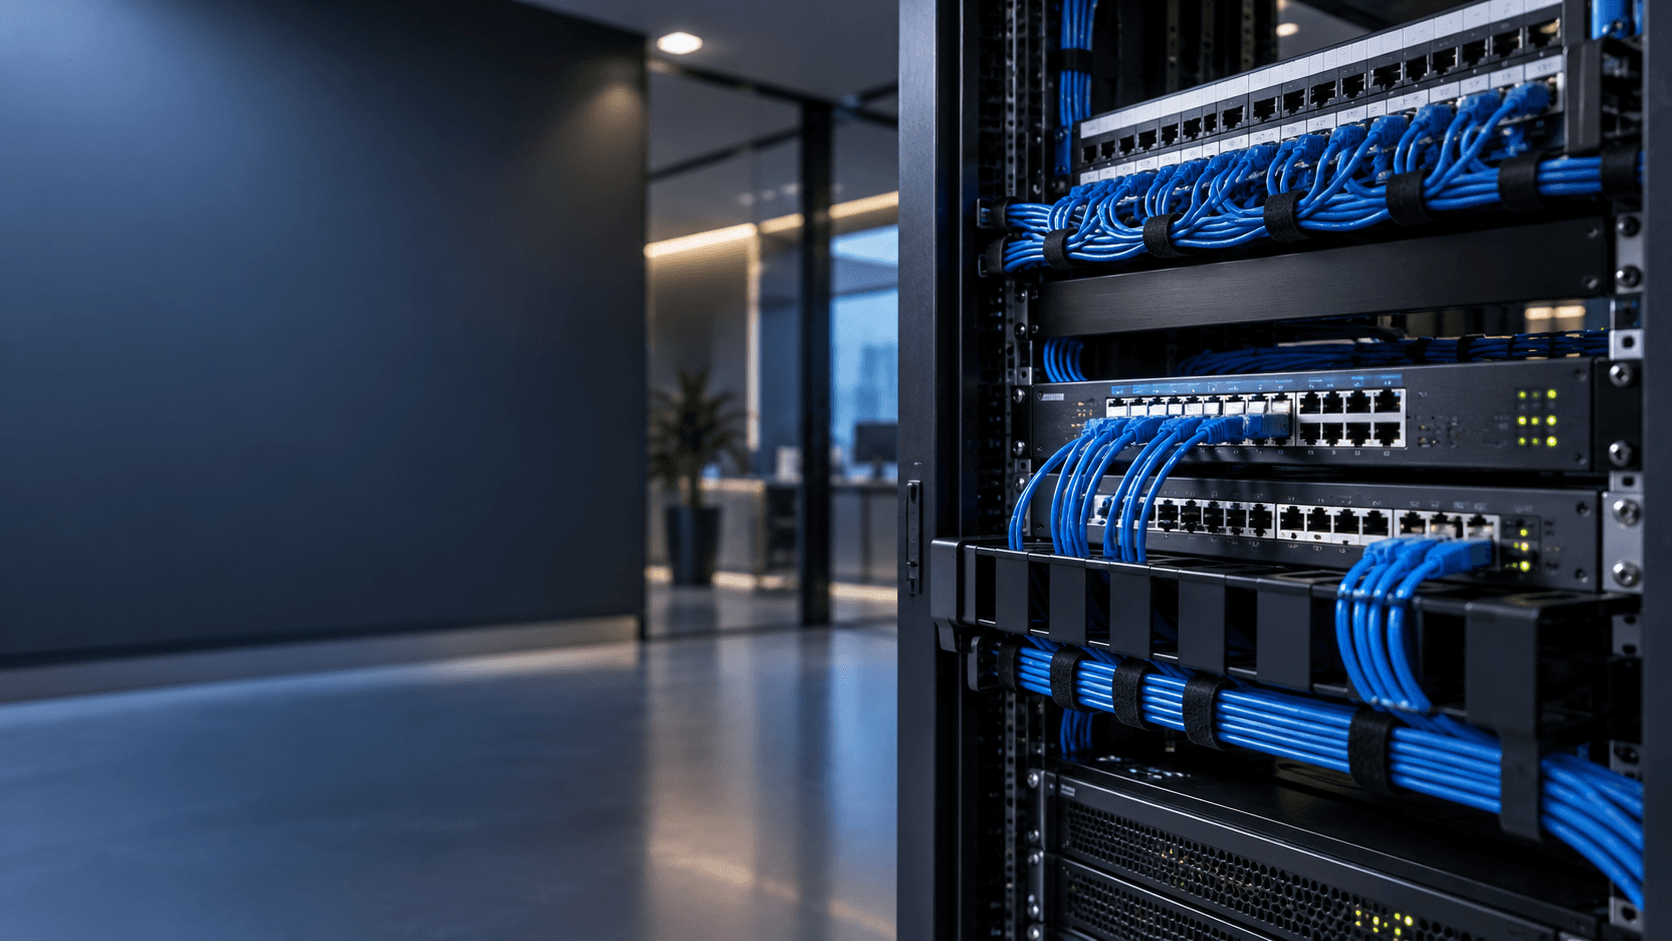
Business network rack with switches, patch panels and organized Ethernet cabling

Firewall & Network Security Solutions

Perimeter protection. Controlled access. Connected infrastructure.

Traffic policiesNetwork zonesSecure access

One controlled network

Security at the edge of your business network.

A firewall acts as a critical control point between your internal systems and external networks. Hyper-Access helps organizations deploy and configure firewall infrastructure that supports controlled access, network visibility, secure connectivity, and protection for business systems.

Our firewall installation offering includes Sangfor solutions, with setup and integration into existing business infrastructure.

01

Network Firewall Protection

Control traffic entering and leaving your network.

Deploy firewall infrastructure that helps regulate network communication according to your organization's security requirements.

  1. External traffic
  2. Firewall policies
  3. Business network
  • Inbound traffic control
  • Outbound traffic control
  • Firewall rule configuration
  • Network access policies
  • Application and service restrictions
  • Port and protocol management
  • Perimeter network protection
  • Security policy configuration
  • Firewall monitoring
  • Configuration maintenance
Explore Firewall Solutions
02

Network Segmentation

Separate critical systems from everyday traffic.

Organize business networks into controlled segments so workstations, servers, POS systems, CCTV, guest Wi-Fi, and other devices do not all operate within the same unrestricted network environment.

  1. Separate network zones
  2. Security gateway
  3. Policy-controlled access
  • VLAN-based segmentation
  • Department network separation
  • Server network isolation
  • POS network segmentation
  • CCTV and IoT separation
  • Guest network isolation
  • Inter-network access policies
  • Controlled internal communication
  • Segmented Wi-Fi environments
  • Policy-based access between network zones
Explore Network Security
03

Secure Remote Connectivity

Give authorized users safer access to business resources.

Support remote work and multi-site operations with properly configured secure network connectivity.

  1. Branches / remote users
  2. VPN gateway
  3. Main office resources
  • VPN connectivity
  • Site-to-site VPN
  • Remote-user access
  • Branch connectivity
  • Encrypted communication
  • Access-control policies
  • Remote connectivity configuration
  • Secure network tunneling
  • Connectivity troubleshooting
Explore Secure Connectivity

Assessment to ongoing support

Built around your actual network environment.

Every business has different users, applications, devices, locations, and security requirements. Hyper-Access evaluates the network first before configuring security controls.

  1. STEP 01

    Security Assessment

    Review the existing network, internet connectivity, critical systems, users, devices, and current security configuration.

  2. STEP 02

    Security Architecture

    Plan firewall placement, network zones, access policies, segmentation, and connectivity requirements.

  3. STEP 03

    Deployment & Configuration

    Install and configure firewall appliances, network interfaces, policies, VPNs, and supporting infrastructure.

  4. STEP 04

    Testing & Validation

    Verify internet access, internal communication, security policies, remote connectivity, and required business applications.

  5. STEP 05

    Support & Optimization

    Maintain and adjust security configurations as users, devices, applications, and business requirements change.

Security ecosystem

One security layer protecting multiple business systems.

The firewall controls traffic between external networks and your internal infrastructure. Security policies determine how systems communicate, while network zones separate critical systems.

  1. Internet / External Network
  2. Firewall & Security Gateway
  3. Core Network
  • Servers
  • Workstations
  • POS
  • CCTV
  • Biometrics
  • Wi-Fi
  • Business Apps
Connected through the core network. Separated into zones. Access governed by policy.

Business security benefits

Better control. Better visibility. Better network organization.

Centralized Security Policies

Manage how devices, services, and network segments communicate through a structured policy framework.

Controlled Network Access

Restrict unnecessary or unauthorized communication between internal and external systems.

Safer Network Segmentation

Separate important systems to reduce unnecessary exposure between devices and departments.

Secure Branch & Remote Access

Provide protected connectivity for approved remote users and additional business locations.

Easier Security Management

Maintain firewall rules, network zones, and access policies through a structured security architecture.

Practical use cases

Network security for real business operations.

01

Protecting Business Internet Access

Control how internal users and devices communicate with external networks.

02

Server Protection

Place business servers within controlled network zones and restrict unnecessary access.

03

POS Network Segmentation

Separate point-of-sale terminals from guest, office, and general-purpose networks.

04

CCTV & IoT Isolation

Keep cameras and other connected devices within dedicated network segments.

05

Guest Wi-Fi Isolation

Separate visitor wireless traffic from internal business resources.

06

Multi-Branch Connectivity

Connect approved business locations through secure site-to-site network connections.

07

Remote Employee Access

Provide authorized remote users with secure access to required internal resources.

Industries

Designed for different operating environments.

  • Corporate Offices
  • Retail Stores
  • QSR & Restaurants
  • Warehouses
  • Schools
  • Clinics
  • Hotels
  • Government Offices
  • Professional Services
  • Multi-Branch Businesses
  • Organizations with Remote Users

Integrated infrastructure

Firewall security works best as part of the complete infrastructure.

A firewall is only one part of a secure and manageable business technology environment. Hyper-Access can coordinate firewall security together with LAN, switching, Wi-Fi, servers, storage, CCTV, biometrics, POS, business applications, and branch connectivity.

  1. Internet
  2. Firewall
  3. Core Network

LAN & Switching

POS · CCTV · Biometrics

Business Wi-Fi

Users · Branch Connectivity

Servers & Storage

Business Applications · Data

Why Hyper-Access

A security solution designed around your infrastructure.

Network Assessment First

Understand the actual network environment before applying security policies.

Integrated Deployment

Coordinate firewall, switching, Wi-Fi, servers, CCTV, biometrics, and related infrastructure within one implementation.

Structured Configuration

Keep firewall rules, network zones, policies, and connectivity organized and maintainable.

Scalable Security Architecture

Prepare the environment for additional users, devices, applications, branches, and network zones.

Technical Support

Maintain a clear technology partner for configuration changes, troubleshooting, and infrastructure expansion.

Plan your network security

Build a more secure network foundation.

Whether you are protecting a new office, securing an existing network, separating critical systems, connecting branches, or improving remote access, Hyper-Access Solutions can help design and deploy the appropriate firewall and network security infrastructure.